The Shift to the Extended Ecosystem
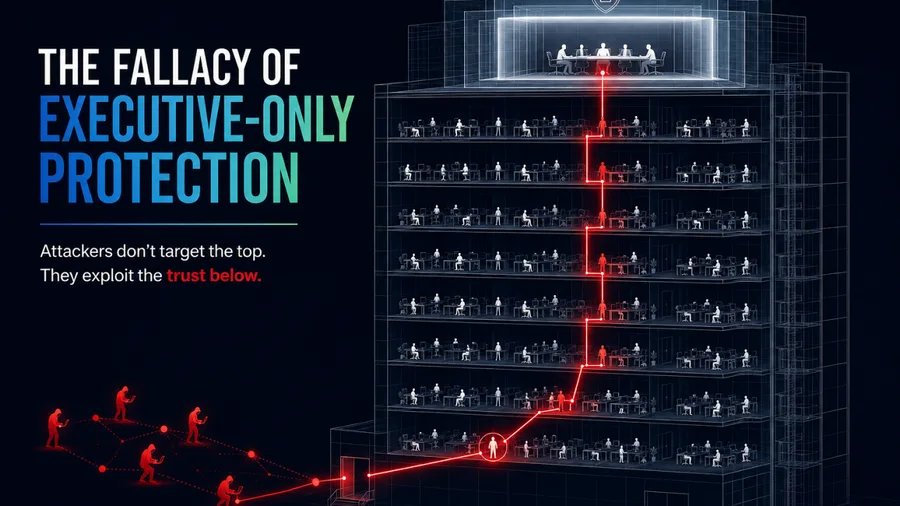
Your vendors are your identity perimeter. Most organizations don't know it yet. Hardening your internal identity perimeter doesn't stop a smart adversary, it just moves him. When you invest heavily in training your employees and protecting internal systems, criminals shift their open-source intelligence gathering away from your direct workforce and turn it outward. They target the contractors, consultants, and external service providers who already hold trusted keys to your network.
This means your attack surface now includes companies you don't control, can't audit on your own schedule, and often don't even fully inventory. You can spend millions of dollars building a strong security culture inside your own payroll, but your network is only as secure as the weakest vendor connected to it. An attacker does not need to spend time trying to break your primary defenses when he can compromise a secondary partner whose identity verifications standards are weak.
Operational Reality: Your identity perimeter does not end at your payroll. When you grant an external partner or contractor trusted access to your internal systems, you inherit their entire identity verification architecture. A sophisticated adversary will always target the weakest link in that extended human chain to walk past your defenses.
The Vulnerability of Inherited Risk
The core flaw in modern architecture is extending implicit trust to external ecosystems. Organizations routinely treat vendor profiles with the same level of network privilege as internal users, without recognizing that a business partner's security posture is now part of their own attack surface. When you provide persistent access to an outside entity, you create a permanent doorway into your environment.
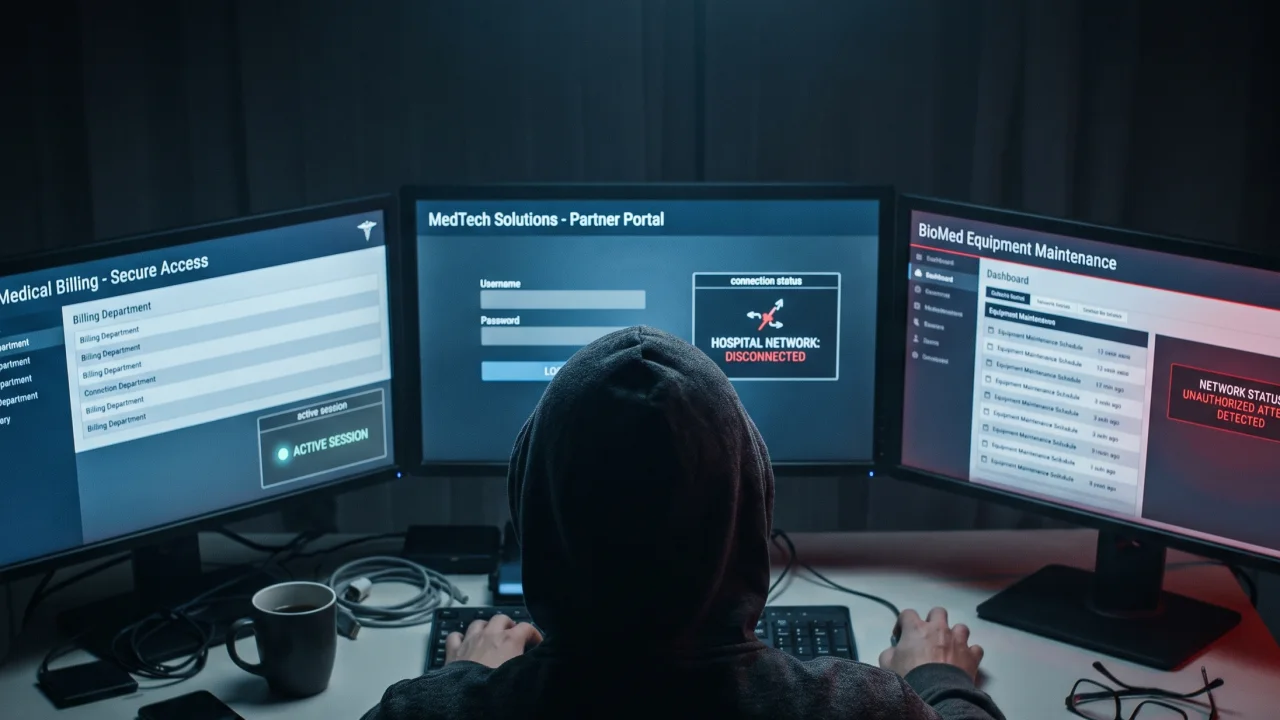
Consider the 2022 compromise of the identity provider Okta. The threat actors did not attempt to breach the core authentication infrastructure directly. Instead, they targeted a third-party customer support vendor. By compromising a single customer service representatives' laptop at the contractor level, the attackers inherited legitimate administrative privileges. They moved past primary perimeter gates and gained deep internal access without raising a single technical alarm.
When an attacker takes over a trusted external connection, traditional monitoring systems see the traffic as completely normal business behavior. The adversary does not need to crack your encryption or steal and executive identity when a third-party contractor can hand them a valid session key.
Restructuring External Verification
Fixing this isn't about better vendor contracts or stronger security questionnaires. It's about refusing to extend trust by default, at every threshold, every time.
Here are three practical rules to secure the extended enterprise:
- Verify Every External Threshold: Treat every incoming third-party connection as entirely unverified. Do not allow external users or contractors to access the internal network without passing through isolated validation gates. Trust must be earned at the perimeter boundary during every single interaction, rather than being granted once at login.
- Restrict Access Boundaries Strictly: Limit vendor profiles exclusively to the specific applications and data required for their immediate role. Cut off all lateral visibility across the network so that a compromise at a secondary partner cannot expose the rest of the enterprise asset footprint.
- Review Session Behavior: Monitor automated actions and access times for unusual patters. If a contractor profile suddenly requests sensitive records or initiates a data transfer at an unusual hour, the architecture must trigger a freeze and review before the threat can spread.
Strategic Governance Takeaway
Governing identity across the extended enterprise is a core business responsibility. As modern adversaries actively shift their focus toward external partners, relying on static compliance checkboxes or standard security questionnaires creates a sever blind spot.
True organizational resilience requires proactive governance over every account that touches your internal network, regardless of whose payroll it sits on. If your security architecture treats external credentials with unquestioned trust, you have not built a perimeter. You have constructed a doorway and handed the keys to someone you do not control.
Originally published on LinkedIn.